Under eIDAS 2.0, high assurance is the highest identity assurance level defined in the regulation. It means that an identity has been verified with the greatest possible certainty, using robust proofing methods and strong multi-factor authentication. High assurance applies when the risk of identity fraud or misuse is significant enough to demand the strongest available safeguards.
The regulation defines three levels of assurance, and high sits at the top. Understanding what it requires, how it differs from the level below it, and where it applies helps organizations decide whether their current identity infrastructure is fit for purpose. The sections below walk through each of these questions in a practical, accessible way.
What are the three assurance levels defined in eIDAS 2.0?
eIDAS 2.0 defines three identity assurance levels: low, substantial, and high. Each level reflects a different degree of confidence in a person’s claimed identity, based on how that identity was verified and how it is authenticated during use. The higher the level, the more rigorous the requirements for both enrollment and ongoing authentication.
The three levels form a tiered framework that organizations and Member States can apply depending on the sensitivity of a service or transaction:
- Low assurance offers a limited degree of confidence. It is suitable for services where the consequences of identity fraud are minimal and basic self-assertion is sufficient.
- Substantial assurance provides a moderate level of confidence. It requires verified identity proofing and multi-factor authentication, making it appropriate for a wide range of online services.
- High assurance provides the greatest degree of confidence. It demands the most stringent identity proofing and the strongest authentication methods, and is reserved for high-risk services and sensitive transactions.
This tiered approach allows organizations to match the level of identity assurance to the actual risk involved in a given interaction. For many regulated sectors such as finance, healthcare, and government, high assurance is not optional but a regulatory expectation.
What specific requirements must an identity scheme meet for high assurance?
To qualify as high assurance under eIDAS 2.0, an identity scheme must meet strict requirements across two dimensions: identity proofing (how the identity is established) and authentication (how the identity is verified at the point of use). Both dimensions must independently satisfy the high assurance criteria.
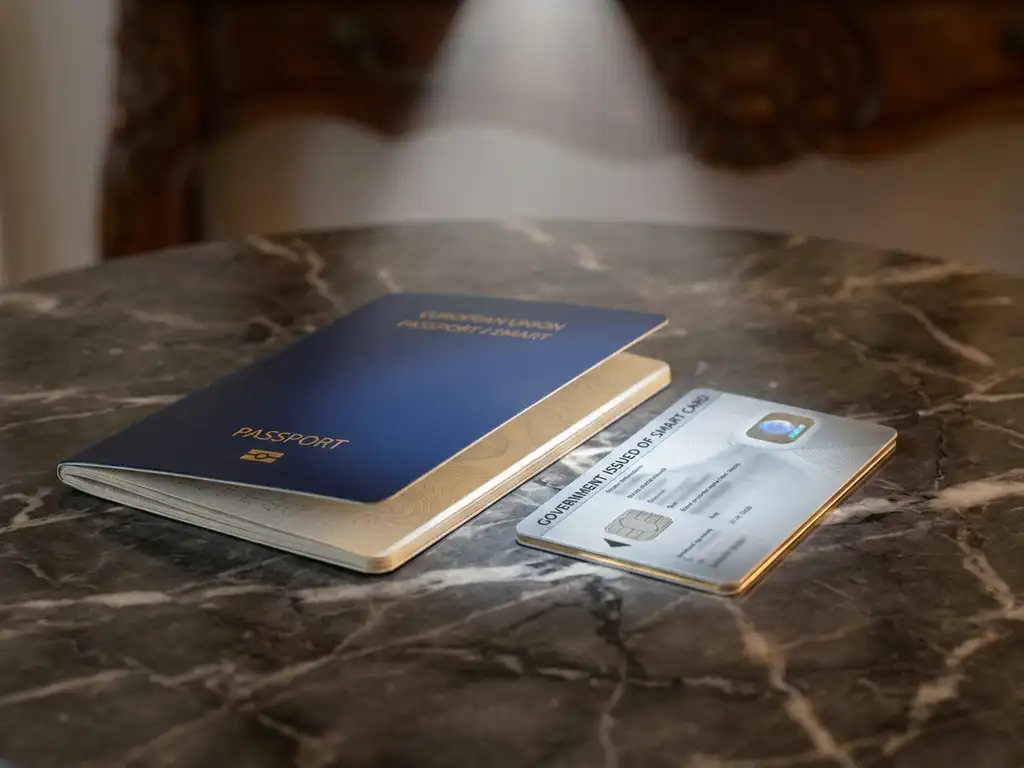
For identity proofing, the scheme must verify that the claimed identity exists and belongs to the person presenting it. This typically involves checking against authoritative sources such as government-issued documents, and confirming that the person presenting the identity is physically the same individual. Remote proofing methods, such as NFC chip reading from a biometric passport combined with liveness detection, are accepted when they meet the required technical standards.
For authentication, high assurance requires the use of multi-factor authentication where at least two independent factors are used. These factors must come from at least two different categories: something you know, something you have, and something you are. The authenticator itself must be hardware-based or cryptographically secured, making it resistant to cloning, phishing, and replay attacks.
The scheme must also demonstrate that the binding between the verified identity and the authenticator is robust. This means the credential issued after proofing must be securely linked to the individual and protected against unauthorized use or transfer.
How does high assurance differ from substantial assurance under eIDAS 2.0?
The key distinction between high and substantial assurance lies in the strength of the authentication mechanism and the rigor of identity proofing. Substantial assurance requires verified identity and multi-factor authentication, but it permits software-based authenticators and allows slightly more flexibility in proofing methods. High assurance requires hardware-backed authentication and leaves no room for weaker alternatives.
In practical terms, a substantial assurance scheme might use a mobile app with a PIN and biometric unlock as the second factor. A high assurance scheme requires that the cryptographic key used for authentication is stored in a hardware security element, such as a secure enclave on a device or a dedicated hardware token, and cannot be extracted or replicated.
The difference also extends to identity proofing. Substantial assurance allows for remote verification methods that are robust but may rely on document scans and video-based checks. High assurance demands a higher level of certainty, often requiring verification against chip-based documents or in-person checks, combined with biometric comparison.
For organizations deciding which level to target, the practical implication is this: if your service involves access to sensitive personal data, financial accounts, healthcare records, or legal transactions, substantial assurance may not be sufficient. High assurance is the appropriate baseline for services where the consequences of identity fraud are severe.
Which authentication methods qualify under the high assurance level?
Under eIDAS 2.0, authentication methods that qualify for high assurance must be hardware-backed, cryptographically secured, and resistant to the most common attack vectors, including phishing, man-in-the-middle attacks, and credential theft. The key requirement is that the private cryptographic key used for authentication is stored in a tamper-resistant hardware element and never leaves it.
Methods that meet this standard include:
- Smart cards and hardware tokens that generate cryptographic signatures using keys stored in a secure chip, such as those used in qualified electronic signature creation devices (QSCDs).
- FIDO2 hardware security keys (such as those conforming to the WebAuthn standard) where the authenticator is a physical device with a dedicated secure element.
- Mobile devices with hardware-backed key storage, where authentication relies on a secure enclave or Trusted Execution Environment (TEE) and is combined with biometric verification tied to that hardware.
- National eID cards with chip-based authentication, where the chip stores cryptographic keys and the card is used in combination with a PIN or biometric factor.
Software-only authenticators, even those using biometrics, do not qualify for high assurance on their own because the keys they protect can potentially be extracted or compromised. The hardware requirement is what sets high assurance authentication apart from the methods permitted at the substantial level.
What does high assurance mean for EUDI Wallet compliance?
The European Digital Identity Wallet, introduced under eIDAS 2.0, is designed to operate at the high assurance level by default. This means that the wallet must meet all the identity proofing and authentication requirements described above, and that any identity data stored or presented through the wallet carries the same level of trustworthiness.
For organizations that accept or rely on the EUDI Wallet for identity verification, this has a direct implication: when a user presents credentials from their wallet, those credentials can be trusted at the high assurance level, provided the wallet has been issued and certified in accordance with the regulation. This removes the need for organizations to re-verify identity from scratch, enabling the kind of reusable, trusted identity that eIDAS 2.0 is designed to support.
Each Member State is required to make at least one certified EUDI Wallet available to citizens, residents, and businesses by 24 December 2026, and public sector services across the EU must accept notified wallets from that date. For regulated private sector organizations in certain sectors — including banking and financial services, healthcare, telecoms, energy, transport, education, social security, drinking water, postal services, digital infrastructure and digital services, and very large online platforms serving more than 45 million users in the EU — a separate acceptance obligation applies from 24 December 2027, under Article 5f of the regulation, in contexts where strong user authentication is legally or contractually required. For organizations preparing their systems today, the 2026 deadline marks the point at which wallets become widely available and acceptance can be tested ahead of the 2027 obligation that applies to relevant private sector parties.
The resources on digital identity available from TrustTech can help organizations understand what wallet readiness looks like in practice and what steps are needed to get there.
Which sectors and use cases require high assurance level identity?
High assurance level identity is required wherever the risk of identity fraud is high and the consequences of getting it wrong are serious. Under eIDAS 2.0, certain services are explicitly required to accept high assurance identities, and in regulated sectors the expectation of high assurance is built into existing legal frameworks that run alongside eIDAS.
Sectors and use cases where high assurance is typically required or strongly recommended include:
- Financial services: Opening bank accounts, accessing investment platforms, executing high-value transactions, and meeting KYC and AML obligations under PSD2 and anti-money laundering directives.
- Government services: Accessing tax records, applying for permits or benefits, signing legal documents, and any interaction with public authorities that involves sensitive personal data.
- Healthcare: Accessing patient records, issuing or claiming prescriptions, providing consent for medical procedures, and sharing health data across borders.
- Pharmaceuticals and life sciences: Regulatory submissions, clinical trial access, and supply chain verification where the identity of authorized individuals must be confirmed with certainty.
- Legal and notarial services: Signing contracts, authenticating legal instruments, and verifying the identity of parties to a transaction.
Organizations in financial services and healthcare in particular are likely to find that high assurance is not a choice but a compliance requirement, both under eIDAS 2.0 and the sector-specific regulations that apply to them.
How TrustTech helps with eIDAS 2.0 high assurance identity
Understanding the requirements for high assurance level identity is one thing. Building the infrastructure to meet them consistently, across onboarding, authentication, and compliance workflows, is where many organizations get stuck. That is where TrustTech comes in.
TrustTech provides a platform built around the eIDAS 2.0 framework, designed to help organizations in regulated sectors implement high assurance identity in a way that is both technically sound and practically manageable. Specifically, TrustTech helps with:
- High assurance identity proofing, including remote verification using NFC chip reading and biometric liveness detection that meets the strictest eIDAS standards.
- Reusable digital identity, so that once a person has been verified at the high assurance level, that identity can be reused across services without requiring them to start from scratch every time.
- EUDI Wallet readiness, ensuring that your organization can receive and verify wallet-based credentials at the high assurance level when the wallet becomes widely available.
- Qualified electronic signatures issued by a Qualified Trust Service Provider, linking identity to every signature and decision in a way that is legally recognized across the EU.
- Sector-specific implementation support for finance, government, healthcare, and other regulated industries.
Whether you are assessing your current identity infrastructure, preparing for eIDAS 2.0 compliance, or looking to build a high assurance onboarding flow from scratch, TrustTech can help you move forward with confidence. Get in touch with TrustTech to discuss your specific situation and find out what high assurance identity looks like for your organization.