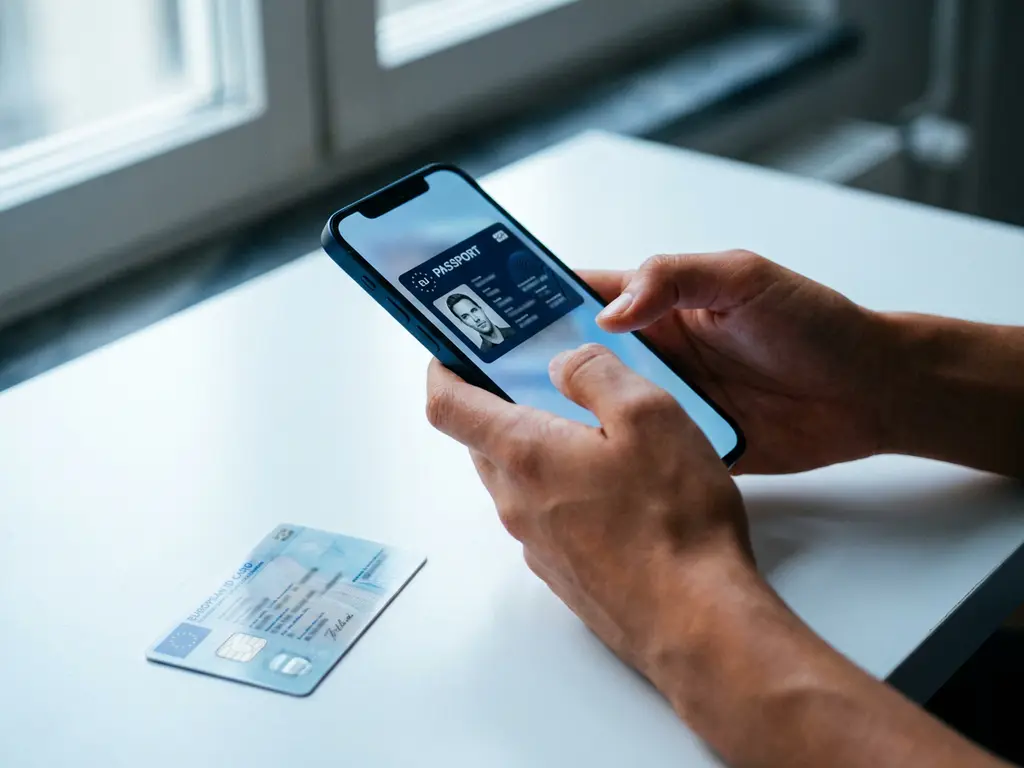
Setting up and activating the EUDI Wallet is a straightforward process: download the official wallet app issued or recognised by your EU Member State, verify your identity using your national eID, and start adding your digital credentials. The process is designed to be accessible to every EU citizen, resident, and business, with privacy and user control built in from the start. Below, we walk through everything you need to know, from eligibility to connecting services.
Who is eligible to use the EUDI Wallet?
Any EU citizen, resident, or business operating within the European Union is eligible to use the EUDI Wallet. Member States are legally required to make the European Digital Identity Wallet available to all who wish to use it, meaning no one can be excluded based on nationality or sector. The wallet is entirely voluntary, so there is no obligation to use it.
This broad eligibility is one of the key principles behind eIDAS 2.0, which amends Regulation (EU) 910/2014 through Regulation (EU) 2024/1183. The goal is to give every person and organisation in the EU access to a single, secure digital identity tool that works across borders and across both public and private services. Whether you are an individual looking to access government services online or a business looking to streamline identity verification for your customers, the wallet is designed with you in mind.
It is worth noting that while Member States are required to provide or mandate a wallet solution, private companies that meet the official recognition criteria can also offer their own wallet solutions. Wallet providers must be certified and notified by the relevant national competent authority before their solution can operate as an EUDI Wallet. This opens up the ecosystem while maintaining consistent security and interoperability standards across the EU.
What do you need before setting up the EUDI Wallet?
Before setting up your EUDI Wallet, you need a compatible smartphone, a valid national identity document, and access to your country’s recognised eID scheme. These three elements allow you to download the wallet app and complete the identity verification step that activates it. Without a verified identity, the wallet cannot function at the required level of assurance.
Here is a quick overview of what to prepare:
- A compatible mobile device: Most modern smartphones running a recent version of iOS or Android will work. Check your national wallet provider’s requirements for specific version support.
- A valid identity document: This is typically a national ID card or passport. Many verification flows use NFC-enabled documents, which allow your phone to read the chip in your document securely.
- Access to your national eID: This might be a government-issued app, a bank ID, or another recognised identity scheme in your country. Note that existing national eID systems are not automatically the same as an EUDI Wallet. Check whether your country’s wallet solution has been certified and notified under eIDAS 2.0.
- A stable internet connection: The initial setup and identity verification require a reliable connection to complete the process correctly.
Some Member States may have additional requirements depending on their national implementation. It is always a good idea to check the official guidance from your country’s wallet provider before you begin.
How does the EUDI Wallet activation process work?
The EUDI Wallet activation process involves downloading the official app, verifying your identity through your national eID scheme, and confirming your account. Once your identity is verified and linked to the wallet, it is activated and ready to use. The entire process is designed to be completed on your smartphone without needing to visit a government office.
Here is how the activation process typically unfolds:
- Download the wallet app: Find the official EUDI Wallet app offered or recognised by your Member State in your app store. Make sure you are downloading from a trusted, official source.
- Create your wallet account: Open the app and follow the onboarding steps. You will be asked to set up a PIN or use biometric authentication to secure your wallet.
- Verify your identity: This is the most important step. You will typically be guided through an identity verification flow using your national eID, which may involve scanning your identity document using NFC, completing a video or selfie check, or authenticating through an existing government or bank ID.
- Receive your Person Identification Data (PID): Once your identity is verified, your wallet receives a certified PID issued by the authorised PID issuer in your Member State. This certified PID is the digital representation of your verified identity and is what makes your wallet legally recognised.
- Activate and start using the wallet: With your PID in place, your wallet unit is active. You can now begin adding attestations and using it for digital services.
The technical backbone of this process is built on the Architecture and Reference Framework (ARF) developed by the EU. The ARF provides the technical elaboration of the requirements set out in the legally binding implementing acts adopted by the European Commission, ensuring that every certified wallet, regardless of which country or provider issues it, meets the same security and interoperability standards.
Which credentials can you store in the EUDI Wallet?
The EUDI Wallet can store a wide range of digital attestations, including government-issued documents, professional qualifications, health records, and financial credentials. These attestations are issued by authorised public authorities or trusted private organisations acting as attestation issuers. Attestations fall into distinct categories: Qualified Electronic Attestations of Attributes (QEAA), issued by qualified trust service providers; Public Body Electronic Attestations of Attributes (PuB-EAA), issued by or on behalf of public bodies; and non-qualified EAA, issued by other recognised providers. The wallet is designed to hold any attestation that has been officially issued within the trust framework.
Based on the use cases tested in the EU’s large-scale pilot programmes, the following types of credentials are among those supported:
- National identity documents and Person Identification Data (PID)
- Mobile driving licences
- Educational diplomas, degrees, and certificates
- Medical prescriptions and the European Health Insurance Card
- Travel documents and digital travel credentials
- Social security information and benefits access
- Proof of organisational representation
- Payment verification credentials
What makes this particularly powerful is that you can share only the specific information a service needs, without revealing anything extra. For example, you can prove you are above a certain age by selectively disclosing an attribute such as “over 18” without sharing your full date of birth, or confirm your nationality without sharing your home address. This selective disclosure is one of the core privacy features of the European Digital Identity Wallet.
How do organisations connect their services to the EUDI Wallet?
Organisations connect their services to the EUDI Wallet by registering as a relying party under CIR (EU) 2025/848, adopted on 6 May 2025, integrating with the wallet’s technical protocols, and operating within the trust framework established under eIDAS 2.0. This allows them to request and verify attestations from wallet holders in a secure, standardised way. Both public sector bodies and private companies can become relying parties.
The integration process involves several important steps. First, an organisation must assess which attestations it needs to request from users and what use cases the wallet will support, for example, customer onboarding, age verification, or contract signing. Under CIR (EU) 2025/848, a relying party must register with the national authority of its Member State of establishment before it can request wallet data. Registration is per intended use: the organisation declares which attributes and attestations it will request, and the wallet checks each request against that registered scope. Next, the organisation needs to align its technical systems with the wallet’s protocols, as elaborated in the Architecture and Reference Framework. This includes implementing the correct data formats, communication standards, and security requirements set out in the applicable implementing acts.
It is also important to understand that relying party registration is tied to the national registration framework of the Member State of establishment. A single registration does not automatically cover every Member State, and organisations operating across multiple Member States may need to account for country-specific registration processes. Sector-specific legislation, in areas such as financial services, healthcare, or government, continues to apply alongside the eIDAS 2.0 framework.
A relying party does not choose a wallet provider. It must be able to accept every relevant notified wallet, regardless of which provider issued it. A relying party also does not automatically need a qualified trust service provider (QTSP) for wallet acceptance. A QTSP becomes relevant in specific scenarios, such as qualified signing or the issuance of qualified attestations.
Organisations operating in regulated sectors such as financial services, government, or healthcare have additional compliance considerations to work through. For instance, financial services organisations need to understand how the EUDI Wallet interacts with existing requirements around strong customer authentication and know-your-customer processes, where the applicable legal basis for processing is typically a legal obligation under AML legislation, which is governed by AML rules and not by eIDAS itself.
From a user experience perspective, organisations should also think about how they present the wallet as an authentication or verification option within their own digital journeys. Each time a user authenticates, they approve a presentation from their wallet. A smooth, well-designed integration builds trust and encourages adoption among users.
What are the acceptance deadlines for relying parties?
The acceptance obligations under eIDAS 2.0 follow a phased timeline, and the deadlines differ between public and private relying parties.
From 24 December 2026, public sector bodies must accept notified EUDI Wallets for online services that require electronic identification. This is the deadline by which Member States must also make the wallet available to citizens and businesses who wish to use it.
From 24 December 2027, the acceptance obligation under Article 5f of eIDAS 2.0 applies to relevant private sector relying parties in regulated sectors where strong user authentication is required by law or by contract. The sectors covered include banking and financial services, healthcare, telecoms, energy, transport, education, social security, drinking water, postal services, digital infrastructure, and digital services. Micro and small enterprises are exempt: the exemption applies to organisations with fewer than 50 employees and an annual turnover or balance sheet total of no more than 10 million euros.
Very large online platforms (VLOPs) are subject to a separate provision under Article 5f. For VLOPs, the obligation applies where the platform requires user authentication, on the voluntary request of the user and limited to the minimum necessary data. The condition relating to legally or contractually required strong authentication does not apply to VLOPs.
What are the most common issues when setting up the EUDI Wallet?
The most common issues when setting up the EUDI Wallet include identity verification failures, incompatible devices or software versions, and difficulties connecting to national eID schemes. Most of these problems are solvable with the right preparation and troubleshooting steps. Understanding them in advance saves time and frustration.
Here are the issues users and organisations encounter most often, along with practical guidance:
Identity verification not completing: This often happens when the identity document being used does not have an NFC chip, or when the chip cannot be read correctly. Make sure your document is NFC-enabled and that you are holding it flat against the back of your phone during the scan. Some cases also involve expired documents, which will cause the verification to fail.
App compatibility issues: Older smartphones or outdated operating systems may not support the security features the wallet requires. Check the minimum device requirements listed by your wallet provider before starting the setup process.
National eID scheme not recognised: If you are trying to use an eID from one country while physically in another, there can be temporary recognition gaps depending on the implementation and certification status of cross-border interoperability in that Member State. The EUDI Wallet framework is designed so that a certified wallet from one Member State can be used with an appropriate relying party in another Member State, but cross-border use cases will become available in phases rather than all at once. This is an area the large-scale pilots actively worked to address.
Credential issuance delays: After identity verification, some attestations may take time to be issued, particularly if they come from government systems that need to process the request. This is normal and usually resolves within a short period.
Verification of attestations: When a relying party verifies an attestation, this involves more than a single check. The process covers three distinct steps: verifying the issuer’s signature against the relevant national trusted list, which is part of the EU List of Trusted Lists (LOTL); checking the revocation status using the issuer’s status information; and validating the wallet unit attestation to confirm that the presenting wallet instance is running on a certified wallet solution. Only the first of these steps can be performed fully offline. Organisations should design their verification flows accordingly.
For organisations integrating wallet support into their services, common issues include misconfigured trust anchors, incorrect data format mappings, and gaps in the user-facing flow that cause confusion. Thorough testing in a sandbox environment before going live is strongly recommended.
How the ID Connector supports EUDI Wallet setup and integration
The ID Connector is an integration that lets relying parties accept every certified European wallet, whatever Member State issued it, for identification, login and qualified signing. EUDI Wallet acceptance comes first; the same interface also carries other IDs, such as national eIDs, bank IDs and identity documents, inside and outside the EU.
For organisations working through the steps described in this article, the ID Connector handles the technical layers that make wallet acceptance work in practice:
- Trust management and trusted list verification: The ID Connector verifies issuer signatures against the relevant national trusted lists, which are part of the EU List of Trusted Lists (LOTL), so your service can confirm the origin and integrity of every attestation presented.
- Revocation checking: The ID Connector checks the revocation status of attestations using the issuer’s status information, covering one of the three verification steps that relying parties need to perform.
- Wallet unit attestation validation: The ID Connector validates the wallet unit attestation to confirm that the presenting wallet instance is running on a certified wallet solution.
- Registered attribute scope enforcement: The ID Connector aligns requests with the attributes and attestations registered under CIR (EU) 2025/848, so that each request stays within the declared scope.
- Qualified signing via a connected QTSP: For use cases that require a qualified electronic signature, the ID Connector connects to an accredited QTSP. TrustTech does not itself issue qualified electronic signatures.
- Sector coverage: The ID Connector is designed for relying parties in financial services, healthcare, pharma, and government, where the combination of wallet acceptance, attestation verification, and compliance with sector-specific legislation matters most.
If you are preparing your organisation for wallet acceptance, whether as a public body facing the 24 December 2026 deadline or as a regulated private sector organisation working toward 24 December 2027, contact TrustTech to find out how the ID Connector fits your integration.