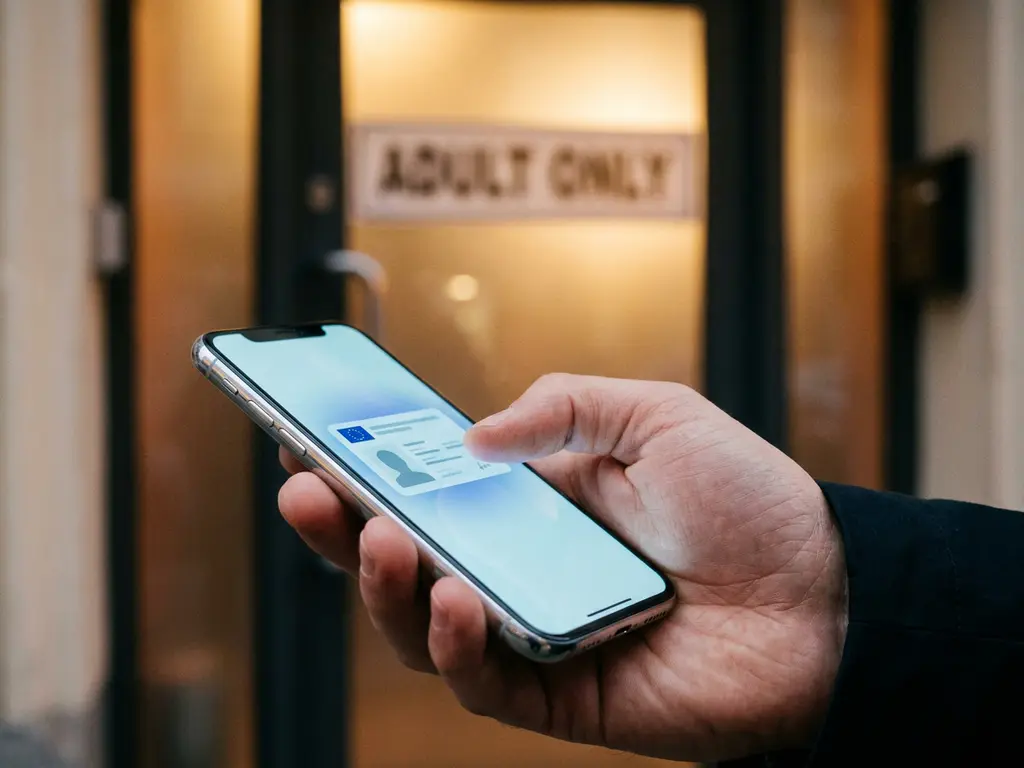
Yes, the EUDI Wallet can be used for age verification online. The wallet allows users to share a simple age confirmation, such as “I am over 18,” without revealing their full date of birth or any other personal details. This makes it one of the most privacy-friendly and technically reliable methods of digital age verification available in Europe today.
As eIDAS 2.0, Regulation (EU) 2024/1183, reshapes how identity data is exchanged across the EU by amending Regulation (EU) 910/2014, age verification is one of the most practical and immediately relevant use cases the European Digital Identity Wallet supports. The sections below walk through how it works, how it compares to existing methods, and what organisations need to do to be ready.
Which age verification use cases does the EUDI Wallet support?
The EUDI Wallet supports age verification in any online or in-person context where a service needs to confirm that a user meets a minimum age threshold. The wallet allows users to present a verified, cryptographically signed attestation that they are above a certain age, and nothing more. This selective disclosure capability makes the wallet suitable for a wide range of practical situations.
Some of the most relevant age verification use cases include:
- Accessing age-restricted content or platforms online, such as streaming services, gambling sites, or adult content
- Purchasing age-restricted products in e-commerce, such as alcohol, tobacco, or medications
- Registering for services that require users to be above a minimum age, such as financial products or social media platforms
- Verifying age at physical points of sale or event entry using the same wallet on a mobile device
- Accessing healthcare services or claiming prescriptions where age-based eligibility applies
The Large Scale Pilots that tested the EUDI Wallet across Europe explored many of these scenarios. The four original pilots ran from April 2023 to 2025 and involved over 350 entities from 26 Member States, covering sectors including financial services, healthcare, and government services. They provided real-world evidence that age verification is a core and viable wallet function. A second wave of pilots started in 2025, with WE BUILD focusing on business wallets and payments, and APTITUDE covering travel, ticketing, vehicle registration, and payments.
How does age verification work inside the EUDI Wallet?
Age verification inside the EUDI Wallet works through selective disclosure. When a service requests an age check, the wallet does not send a date of birth. Instead, it sends a cryptographically signed response to a specific question, for example: “Is this user 18 or older?” The answer is yes or no, derived from the user’s government-issued identity data stored in the wallet. Proving age above a threshold through selective disclosure of a single attribute does not require zero-knowledge proofs.
The underlying identity data in the wallet is issued and certified by a trusted authority, such as a national government or an officially recognised identity provider. This means the age attestation carries the same legal weight as a physical identity document, with far less personal data exposed.
The user remains in control throughout the process. Before any data is shared, the wallet presents a clear consent screen showing exactly what information will be disclosed and to whom. The user must actively approve each transaction. Nothing is shared automatically or without that explicit approval. Note that approving a data request in the wallet is a separate matter from consent as a legal basis under the GDPR: the organisation receiving the data still needs its own lawful basis for processing.
Verifying an age attestation involves three distinct checks. First, the verifier checks the issuer’s signature against the relevant national trusted list, which is part of the EU List of Trusted Lists. This check can be performed offline. Second, the verifier checks the revocation status of the attestation using status information provided by the issuer, which requires contact with the issuer’s infrastructure. Third, the verifier checks the wallet unit attestation to confirm that the presenting wallet runs on a certified wallet solution. These three checks together provide the assurance that the attestation is genuine, current, and presented by a legitimate wallet unit.
This approach is technically grounded in the Architecture and Reference Framework developed by the eIDAS Expert Group, which provides the technical elaboration of the requirements set out in the implementing acts that all EUDI Wallets across EU Member States must follow. The ARF is not itself legislation, but it translates the legally binding requirements into the standards that wallet providers, issuers, and relying parties implement in practice. The result is a consistent, interoperable experience regardless of which Member State issued the wallet or which country the service is operating in, though the practical availability of specific cross-border use cases may develop in phases as national rollouts mature.
What is the difference between EUDI Wallet age verification and existing methods?
The key difference is that EUDI Wallet age verification shares only what is strictly necessary, while most existing methods share considerably more. Traditional age checks typically require users to upload a copy of their passport or driving licence, submit a full date of birth, or go through a third-party verification service that processes and stores personal data. The EUDI Wallet replaces all of this with a single, privacy-preserving confirmation.
Existing methods and their limitations
Current approaches to online age verification range from self-declaration (simply ticking a box to confirm age) to document upload, credit card checks, and third-party identity verification services. Self-declaration offers no real assurance. Document uploads create data security risks and friction for users. Third-party services often involve extensive personal data processing, raising compliance questions under the GDPR.
What the EUDI Wallet does differently
The EUDI Wallet is built on government-verified identity data, which means the age attestation is legally reliable and not self-reported. At the same time, the selective disclosure model ensures that only the minimum necessary information is shared. A cinema, an online retailer, or a gaming platform receives confirmation that the user is over the required age threshold, and nothing else. No name, no address, no date of birth.
This combination of high assurance and minimal data exposure addresses both the reliability problem of self-declaration and the privacy problem of document-based verification. For organisations operating under financial compliance or data protection requirements, this is a meaningful improvement over legacy methods.
Which sectors are required to accept the EUDI Wallet for age checks?
Under eIDAS 2.0, certain categories of online service providers will be required to accept the EUDI Wallet as a valid method of identity and attribute verification, including age. The scope and timing of these obligations differ between the public and private sectors, and the specific requirements continue to be defined through implementing acts adopted by the European Commission.
24 December 2026 is the legal deadline by which every EU Member State must have at least one certified EUDI Wallet available to citizens, residents, and businesses, and public sector bodies must accept notified wallets as a valid means of identification from that date. This deadline relates to wallet issuance obligations and public sector acceptance. It is not a general acceptance deadline for private sector organisations, and it does not guarantee that every national wallet will have reached the same level of maturity or that every cross-border use case will be fully operational across all Member States on that date. Practical interoperability and national rollout are expected to develop in phases.
For private sector organisations, a separate acceptance obligation applies from 24 December 2027, under Article 5f of the eIDAS 2.0 regulation, within contexts where strong user authentication is legally or contractually required. Very large online platforms with more than 45 million users in the EU fall under a separate provision of Article 5f: for those platforms, the obligation applies where the platform requires user authentication, on the voluntary request of the user, and limited to the minimum necessary data. The condition of legally or contractually required strong authentication does not apply to very large online platforms. Micro and small enterprises, defined as organisations with fewer than 50 employees and an annual turnover or balance sheet total not exceeding 10 million euros, are excluded from the Article 5f obligation.
The regulated private sectors subject to that 2027 acceptance obligation include:
- Banking and financial services, where age determines product eligibility and strong authentication is required
- Healthcare and pharmacy services, where certain products and services are age-restricted
- Telecommunications providers operating under regulated authentication requirements
- Energy suppliers and providers within regulated frameworks
- Transport services subject to strong authentication obligations
- Education and social security services where age-based eligibility applies
- Drinking water, postal, and digital infrastructure services within regulated contexts
- Very large online platforms with more than 45 million users in the EU, including those subject to the Digital Services Act’s age assurance requirements for minors
For organisations in healthcare and government services, the timelines are particularly relevant. Public sector bodies must be ready to accept notified wallets by 24 December 2026, while regulated private sector organisations in the categories listed above must be ready to accept the wallet by 24 December 2027. These are legal deadlines, not predictions of a single European go-live moment. Organisations should plan for a phased environment and begin preparing well in advance of whichever deadline applies to them.
What do organisations need to implement EUDI Wallet age verification?
To accept EUDI Wallet age verification, an organisation needs to become a recognised relying party. Under CIR (EU) 2025/848, adopted on 6 May 2025, a relying party must register with the national authority of the Member State in which it is established before it can request wallet data. Registration is per intended use: the relying party specifies which attributes and attestations it will request, and the wallet checks each request against that registered scope. A relying party does not choose a wallet provider. It must be able to accept every relevant notified wallet, regardless of which provider issued it.
In practical terms, the implementation journey involves several steps. Organisations need to understand the Architecture and Reference Framework, which provides the technical elaboration of how wallets and relying parties interact. They need to update their user flows to support wallet-based interactions, including the approval screens that users see before sharing any information. Sector-specific legislation continues to apply alongside the eIDAS 2.0 requirements. A relying party does not automatically need a qualified trust service provider for wallet acceptance. A QTSP becomes relevant in specific scenarios, such as qualified signing or the issuance of qualified electronic attestations of attributes.
From a compliance perspective, organisations should also review their data minimisation practices. One of the advantages of EUDI Wallet age verification is that it reduces the amount of personal data an organisation needs to collect and store. This can simplify GDPR compliance but may require updates to existing privacy policies, data processing records, and internal procedures. Each organisation remains responsible for establishing its own lawful basis for processing the data it receives.
Technical readiness, regulatory alignment, and user experience design all need to come together. Organisations that start this process early will be better positioned to meet the applicable deadline, whether 24 December 2026 for public sector bodies or 24 December 2027 for regulated private sector organisations in the relevant sectors, and to offer a smooth experience to users who arrive with a wallet.
How TrustTech helps with EUDI Wallet age verification
The ID Connector is an integration that lets relying parties accept every certified European wallet, whatever Member State issued it, for identification, login and qualified signing. EUDI Wallet acceptance comes first; the same interface also carries other IDs, such as national eIDs, bank IDs and identity documents, inside and outside the EU.
For age verification specifically, the ID Connector handles the verification of the issuer’s signature against the relevant national trusted lists, checks the revocation status of the attestation, and validates the wallet unit attestation to confirm the presenting wallet runs on a certified wallet solution. It also enforces the registered attribute scope, so that only the attributes the relying party has registered for a given intended use are requested and received.
Organisations in financial services, healthcare, pharma, and government can use the ID Connector to meet their acceptance obligations under eIDAS 2.0, whether the applicable deadline is 24 December 2026 or 24 December 2027, without building and maintaining that verification infrastructure themselves.
If you want to understand what EUDI Wallet age verification means for your organisation specifically, get in touch with TrustTech to discuss the next steps.