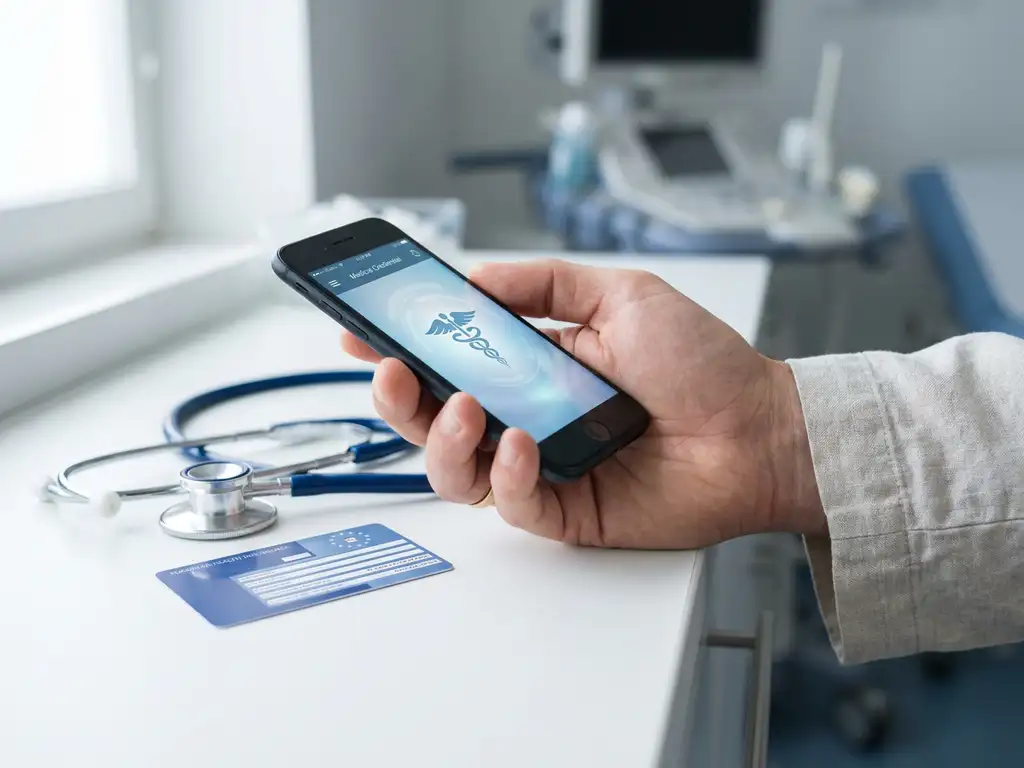
The EUDI Wallet has a direct and meaningful impact on the healthcare sector in Europe. It enables patients to securely store and share health-related credentials, such as prescriptions and insurance cards, while giving them full control over their personal data. For healthcare organizations, it also introduces new obligations around identity verification and compliance with eIDAS 2.0, which amends Regulation (EU) 910/2014. This article addresses the most important questions healthcare professionals and organizations are asking right now.
What data can the EUDI Wallet store and share in healthcare?
The EUDI Wallet can store and share a range of health-related digital documents, including prescriptions, the European Health Insurance Card (EHIC), vaccination records, and other medical credentials. Users can choose exactly which data they share and with whom, disclosing only what is strictly necessary for a given interaction.
This selective disclosure principle is one of the most important features for healthcare. A patient visiting a pharmacy, for example, does not need to share their full medical history. They can present only the relevant prescription details. This approach significantly reduces the risk of unnecessary data exposure and gives patients genuine control over their health information.
The POTENTIAL Large Scale Pilot, which ran from April 2023 to 2025, tested e-prescriptions as a specific use case, involving pharmacies and healthcare providers working together to validate how the wallet handles medical data in real-world scenarios. The insights gathered from that pilot are being used to refine the technical specifications and ensure the system works reliably across borders.
Beyond prescriptions, the wallet can also carry documents that support freedom of movement within the EU, such as the EHIC. This makes cross-border healthcare access more straightforward for patients traveling or living in another Member State, though the practical availability of specific credentials will depend on what each Member State’s wallet solution supports at the time of use.
How does the EUDI Wallet change patient identification in Europe?
The EUDI Wallet changes patient identification by replacing fragmented, paper-based processes with a single, cryptographically secured digital identity. Instead of presenting a physical ID card or insurance document, patients can authenticate themselves through their wallet, which is designed to be accepted across all EU Member States once the relevant relying parties have registered and the applicable cross-border use cases are operational in their jurisdiction.
Today, patient identification in healthcare is inconsistent. Processes vary significantly between hospitals, clinics, and pharmacies, and even more so across national borders. A patient seeking care in another EU country often faces administrative hurdles because their identity documents or insurance credentials are not easily recognized. The EUDI Wallet framework is designed to address this directly, though cross-border availability of specific use cases will develop in phases as national wallet solutions are certified, notified, and adopted by relying parties.
Because the wallet is built on a common technical framework, elaborated in the Architecture and Reference Framework (ARF) and given legal force through implementing acts adopted by the European Commission, a verified credential issued in one Member State can be trusted by an appropriate relying party in another. This is particularly relevant for cross-border patient care, emergency treatment abroad, and telemedicine services that operate across national boundaries. It does not mean that sector-specific legislation disappears or that every credential automatically carries the same legal consequence in every Member State.
For healthcare providers, this shift also means a more reliable and efficient intake process. Manual identity checks are time-consuming and prone to error. Wallet-based verification is faster and tamper-evident, reducing administrative burden and improving the accuracy of patient records from the very first interaction.
What are the GDPR and eIDAS 2.0 compliance implications for healthcare providers?
Healthcare providers that accept or process data from the EUDI Wallet must align with both GDPR requirements and the obligations introduced by eIDAS 2.0. This means ensuring that identity verification processes respect data minimization principles, that consent is properly managed, and that only registered relying parties can request wallet data.
Under eIDAS 2.0 and CIR (EU) 2025/848, adopted on 6 May 2025, organizations that want to request data from a user’s wallet must register as a relying party with the national competent authority of the Member State where they are established. This registration requires specifying, per intended use, which attributes and attestations will be requested. The wallet then checks incoming requests against that registered scope. For healthcare providers, this is a significant operational step that requires preparation well in advance of any implementation. Organizations operating across borders may need to engage with more than one national registration process.
GDPR adds another layer of responsibility. Health data is classified as a special category of personal data under GDPR, which means it carries stricter processing requirements. A relying party needs its own legal basis under Article 6 GDPR for processing wallet-derived data, and a separate condition under Article 9(2) GDPR for health data specifically. Healthcare organizations must be able to demonstrate a clear legal basis for processing wallet-derived health data, maintain records of processing activities, and ensure that their systems support patients’ rights, including the right of access and the right to erasure.
It is also important to distinguish between a user approving a data request in the wallet and consent as a legal basis under GDPR. Each approval in the wallet is a separate user action for that specific transaction. A relying party cannot rely on that wallet approval alone as its GDPR legal basis. The legal basis must be established independently.
The EUDI Wallet is designed with privacy by default. Because users control what they share, the technical architecture naturally supports data minimization. However, healthcare providers still need to update their internal policies, data processing agreements, and staff training to reflect these new workflows. Compliance is not automatic just because the wallet itself is privacy-preserving.
Which healthcare use cases benefit most from the EUDI Wallet?
The healthcare use cases that benefit most from the EUDI Wallet are those involving identity verification, credential sharing, and cross-border access to care. These include prescription claiming at pharmacies, accessing the European Health Insurance Card, patient onboarding at hospitals, and telemedicine identity verification.
Here is an overview of the most impactful use cases in the medical sector:
- Prescription claiming: Patients can present a verified digital prescription directly to a pharmacy, removing the need for paper documents and reducing the risk of fraud or errors.
- European Health Insurance Card (EHIC): The wallet can store a digital version of the EHIC, making it easier for patients to access healthcare services in other EU countries without carrying physical documents, subject to the availability of this credential in their Member State’s wallet solution.
- Patient onboarding: Hospitals and clinics can verify patient identity quickly and reliably at registration, reducing intake time and improving data accuracy.
- Telemedicine services: Digital health platforms can use wallet-based identity verification to confirm who they are treating, which is particularly important for services that operate across borders. Sector-specific rules governing telemedicine remain in force alongside the wallet framework.
- Access to social security and health benefits: Patients can use the wallet to prove eligibility for specific benefits or services without needing to provide extensive documentation each time, where the relevant attestations have been issued by the appropriate national authority.
These use cases share a common thread: they all involve a moment where identity and credentials need to be verified quickly, reliably, and in a way that respects patient privacy. The EUDI Wallet addresses all of these needs within a single, standardized framework. The practical availability of each use case will depend on national rollout progress, relying party adoption, and any sector-specific requirements that apply in a given Member State.
What should healthcare organizations do to prepare for the EUDI Wallet?
Healthcare organizations should start preparing for the EUDI Wallet by assessing their current identity and data infrastructure, registering as a relying party under eIDAS 2.0 and CIR (EU) 2025/848, and updating their compliance frameworks to align with the new requirements. Early preparation reduces risk and positions organizations to benefit from the wallet as national rollouts mature.
Here is a practical sequence of steps to get started:
- Map your current processes: Identify where the EUDI Wallet will have the most impact on patient identification and data sharing workflows.
- Understand the relying party registration requirements: Under CIR (EU) 2025/848, registration is managed by national competent authorities. Requirements may differ by jurisdiction, and organizations operating in multiple Member States may need to register in each of them. Registration includes specifying per intended use which attributes and attestations will be requested.
- Review your GDPR compliance posture: Update your data processing agreements, privacy notices, and internal policies to reflect wallet-based data flows. For health data, ensure you have both an Article 6 and an Article 9(2) GDPR legal basis in place.
- Engage your IT and security teams: Ensure your systems can integrate with wallet-based authentication and that your security architecture supports the required assurance levels. Wallet-based verification involves checking the issuer’s signature against the relevant national trusted list, the revocation status of the attestation, and the wallet unit attestation to confirm the presenting wallet runs on a certified wallet solution.
- Train relevant staff: Clinical and administrative staff need to understand how the wallet works and what it means for their day-to-day interactions with patients.
- Follow the pilot program outcomes: The POTENTIAL Large Scale Pilot tested e-prescriptions and produced valuable insights. Monitor the findings from ongoing pilot activity to inform your own implementation approach.
The legal deadline for Member States to make wallet solutions available is 24 December 2026. From that date, public bodies must accept notified wallets for online services that require electronic identification. For relevant regulated private sectors, including healthcare organizations that require strong user authentication, the acceptance obligation under Article 5f of eIDAS 2.0 applies from 24 December 2027. Micro and small enterprises, defined as organizations with fewer than 50 employees and an annual turnover or balance sheet total not exceeding 10 million euros, are exempt from this private acceptance obligation.
These are regulatory deadlines, not predicted launch dates. Practical interoperability and relying party adoption are expected to develop in phases. Healthcare organizations should not wait for a single European go-live moment. Starting preparation now gives a meaningful advantage: the regulatory framework is maturing, and organizations that have already aligned their processes will be far better positioned than those that delay. For more sector-specific context, the healthcare sector overview provides a useful starting point.
How TrustTech helps healthcare organizations prepare for the EUDI Wallet
The ID Connector is an integration that lets relying parties accept every certified European wallet, whatever Member State issued it, for identification, login and qualified signing. EUDI Wallet acceptance comes first; the same interface also carries other IDs, such as national eIDs, bank IDs and identity documents, inside and outside the EU.
For healthcare organizations, the ID Connector handles several of the most technically demanding parts of wallet-based verification. It checks the issuer’s signature against the relevant national trusted lists, which are brought together in the EU List of Trusted Lists (LOTL). It controls the revocation status of attestations and validates the wallet unit attestation to confirm that the presenting wallet runs on a certified wallet solution. It also enforces the registered attribute scope, so that only the attributes and attestations specified during relying party registration are requested and processed.
In practice, this means a hospital, pharmacy, or digital health platform can connect to the ID Connector and gain the ability to verify patient identity and health-related credentials across wallet solutions and Member States, without building and maintaining that verification infrastructure independently. For use cases involving qualified signing, the ID Connector connects to a qualified trust service provider, enabling qualified electronic signatures where the workflow requires them.
Whether you are exploring what wallet-based patient identification means for your organization or are ready to move into active preparation, TrustTech provides the tooling to support that process. Explore our implementation approach or take a look at how we work with organizations in regulated healthcare environments. Ready to take the next step? Get in touch with TrustTech and let us help you prepare for the future of digital identity in healthcare.